Security and compliance built into the product from the start
Compliance-ready development for HIPAA and GDPR, EU Digital Product Passport software, AI guardrails and security testing for web, mobile, API and cloud.
What we do in Security & Compliance
Software and AI built to HIPAA and GDPR requirements and tested before attackers find the gaps.
Software built to meet HIPAA and GDPR requirements from day one, with audit trails and access control.
Collect supplier data and publish ESPR-compliant product passports with the right access for each stakeholder.
Control what your AI can see, say, and do with policies, filters, and audit trails.
Stress-test your AI for prompt injection, data leaks, and unsafe outputs before attackers do.
Find and fix vulnerabilities in web, mobile, and API applications before they are exploited.
Secure code reviews plus automated SAST and DAST built into your development pipeline.
Identify misconfigurations and access risks across your AWS, Azure, or GCP setup.
Shipped work and accelerators
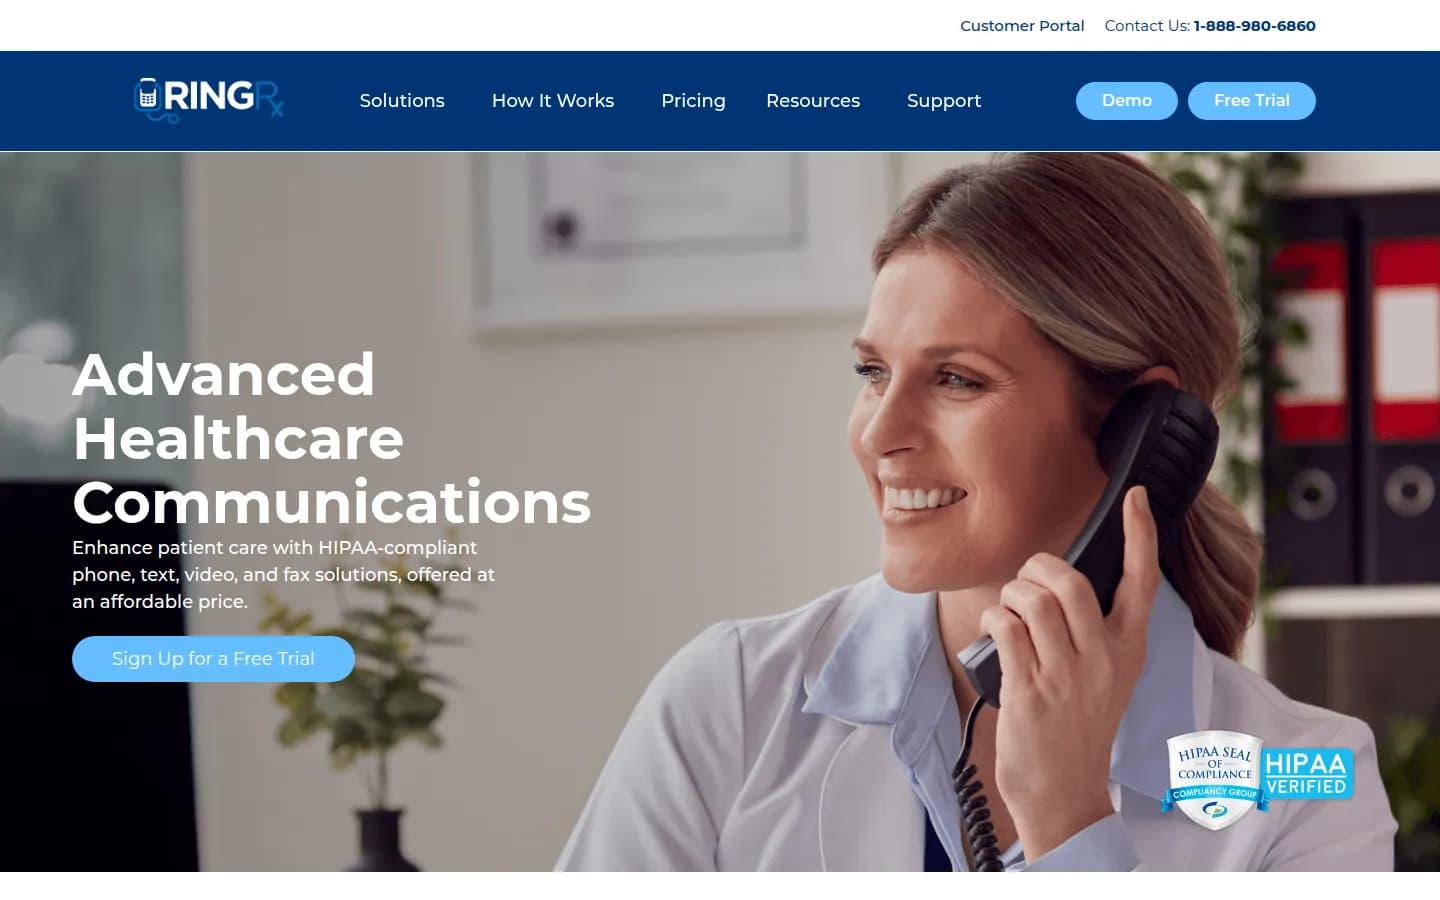
HIPAA phone, SMS, fax & video
One HIPAA-compliant platform for phone, text, fax and video in healthcare practices
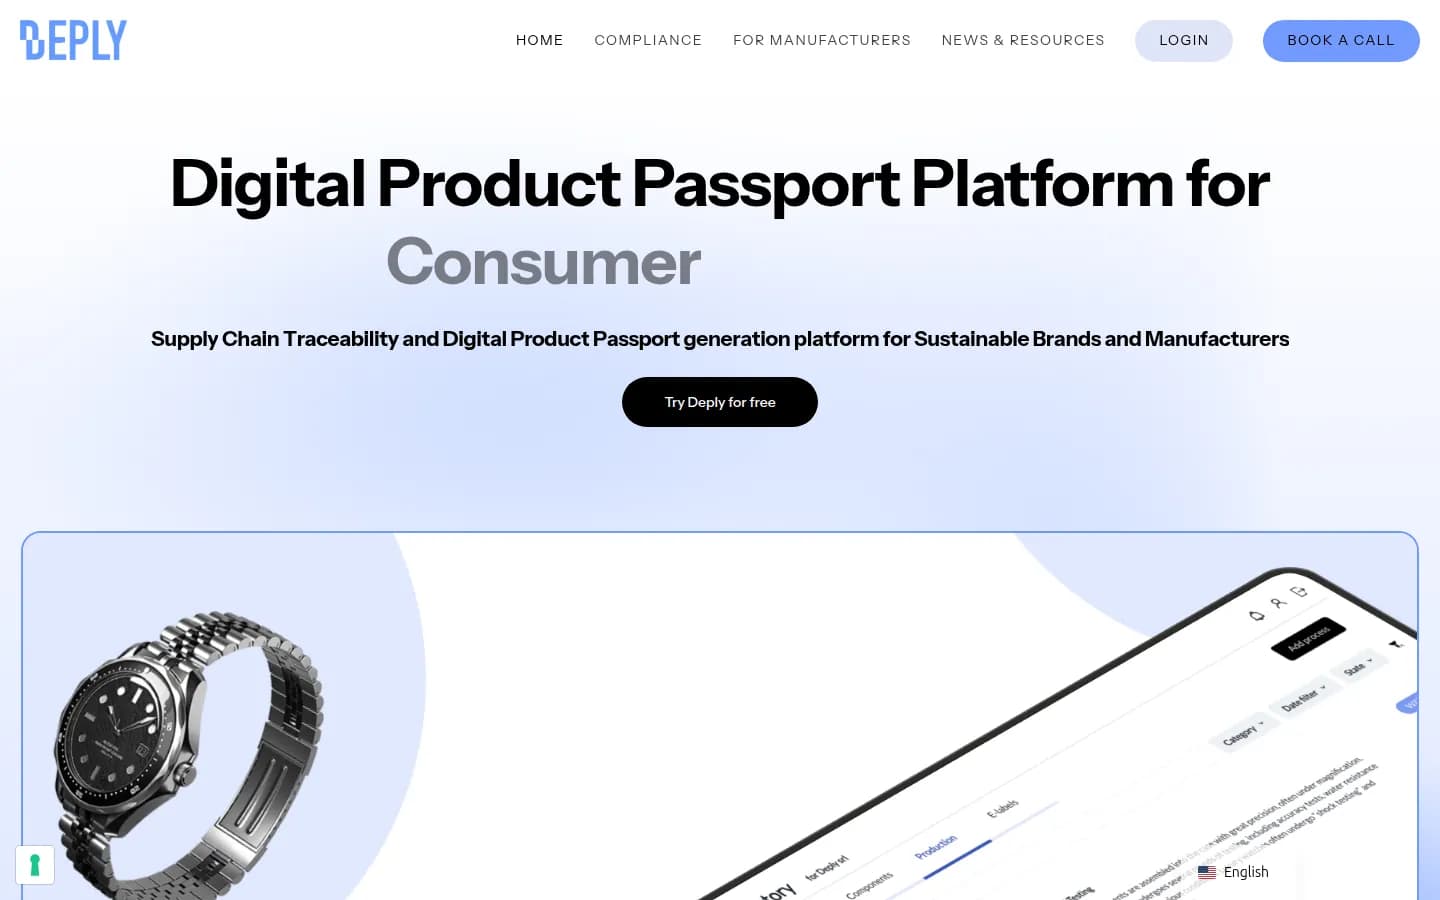
EU Digital Product Passport (ESPR)
An EU Digital Product Passport platform built for ESPR, from onboarding to a published, verifiable passport
AI Booking Agent
An appointment-booking agent that answers, qualifies and books into your calendar over phone or chat.
ChatAI
Our internal builder for knowledge assistants and chatbots trained on your documents and tools.
Decode
A client RAG knowledge assistant with mobile app, retrieval over their content, deployed on AWS Fargate.
Phases, timelines and what you receive
Requirements
Control map (HIPAA, GDPR, ESPR) and architecture
Build or test
Working product or completed security testing
Validate
Findings, fixes, evidence pack and launch checklist
Operate
Monitoring, patching and compliance updates
FAQ for Security & Compliance
Questions specific to security & compliance.
Yes, for engagements involving PHI, and we use BAA-covered hosting and vendors.
Yes, using BAA-covered model providers or self-hosted models so PHI stays protected.
There is no official HIPAA certification. Compliance is shown through controls, policies and evidence, which we build and document.
A digital record of a product's materials, origin, repairability and recyclability required under the EU ESPR, accessible via a data carrier such as a QR code.
Timelines depend on product category and delegated acts. We help you plan to the dates that apply to you.
Yes. Deply is our EU Digital Product Passport platform.
Ready to talk about what to build?
Book a short call with a senior engineer. No pitch deck, just a clear next step.
- We reply within 1 business day.
- NDA available on request
- You own all code from day one