Compliance-ready software for teams handling patient and personal data
Healthcare and EU software with encryption, audit logs, access control and BAA-ready hosting built in from the first sprint and mapped to HIPAA and GDPR.
Does this sound like your team?
“Staff use personal phones or consumer apps to talk to patients”
“An enterprise healthcare customer sent a security questionnaire you can't answer”
“You are not sure your current software is HIPAA compliant”
What you get with Compliance-Ready Development
- HIPAA control mapping for your product
- Encryption in transit and at rest
- Role-based access and audit logs
- BAA-covered hosting and vendors
- Secure messaging, voice, fax and video
- EHR / practice-system integration
- Security review and evidence pack
- Incident and breach runbooks
HIPAA-Compliant AI Checklist
Controls, logging and vendor checks for AI features that may touch PHI.
Phases, timelines and what you receive
Requirements
Control map (HIPAA, GDPR, ESPR) and architecture
Build or test
Working product or completed security testing
Validate
Findings, fixes, evidence pack and launch checklist
Operate
Monitoring, patching and compliance updates
What we measure before Go / Adjust / Stop
Every phase ends with a decision based on numbers agreed at the start.
Controls
every HIPAA safeguard mapped to a feature or process
Access
least-privilege roles tested
Logging
every PHI access is recorded
Vendors
BAAs in place for every service touching PHI
Get a plan for Compliance-Ready Development
A few fields, no sales script. We reply within 1 business day with next steps.
Where we've done this before
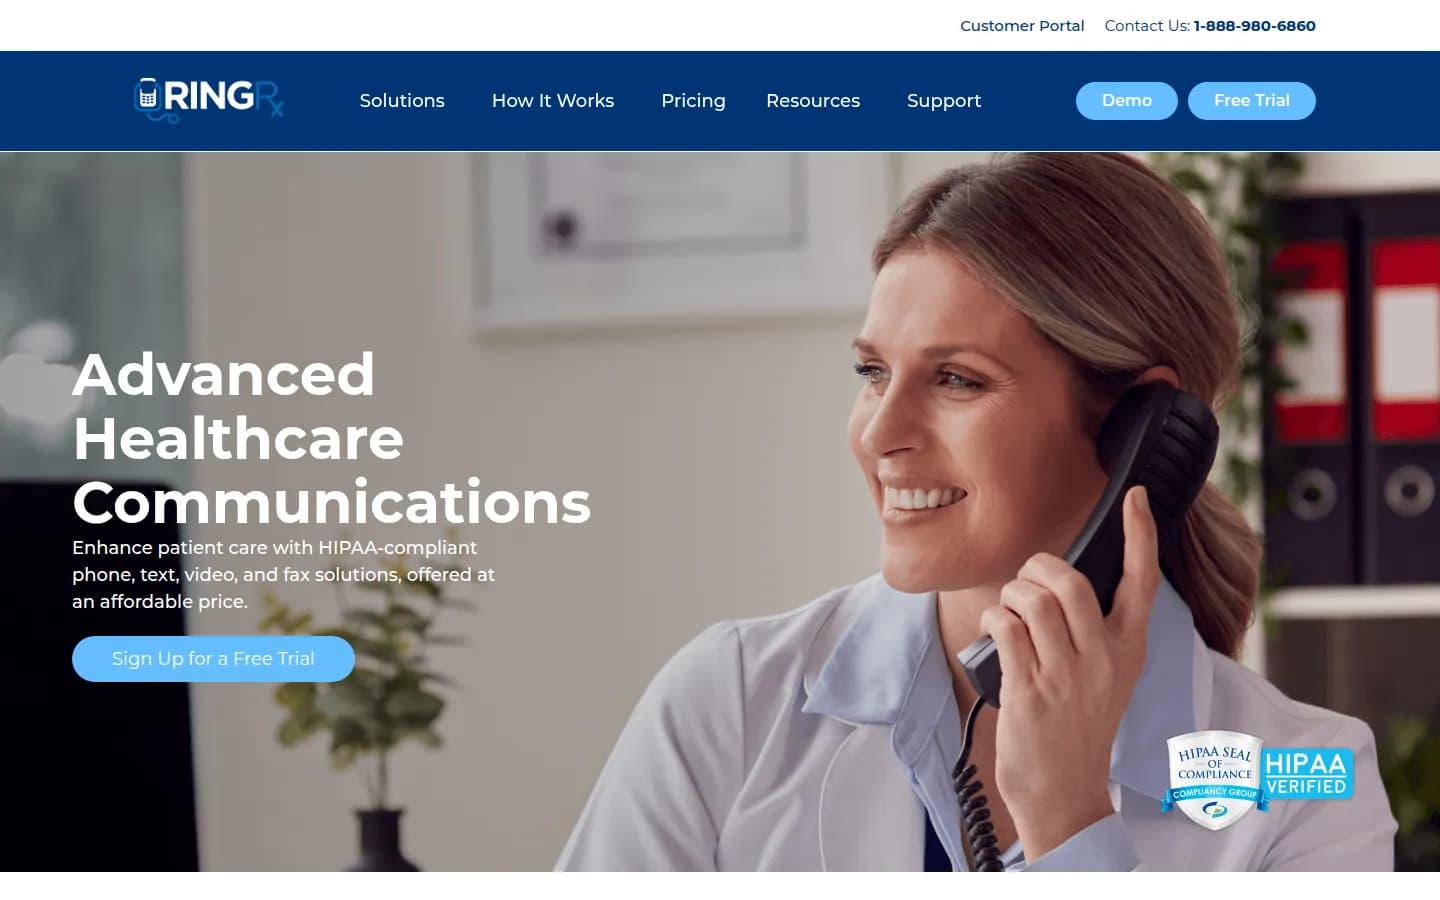
HIPAA phone, SMS, fax & video
One HIPAA-compliant platform for phone, text, fax and video in healthcare practices
Multi-entity compliance
A secure dashboard for owners of multiple companies to track entities, filings and documents
Senior people, named roles
Tech Lead
Architecture and control mapping.
Full-stack Engineers
Product build and integrations.
QA / Security Engineer
Testing, security review and evidence.
What we build with
Industries we deliver this for
Ways to work with us
Every project gets a written quote after a short scoping call.
Fixed-scope project
Clear scope and timeline. Scope agreed before code starts; change requests quoted separately.
Dedicated team / AI Pod
Evolving roadmap or AI systems in production. Monthly, scale up or down with notice.
Support & maintenance retainer
Live products that need fixes, updates, monitoring and small features each month.
Who this is not for, and what we won't do
- We don't send PHI to AI providers without a BAA
- We don't call software 'HIPAA compliant' without the controls to prove it
What clients say
“Working with the Bit & Bytes team on our CRM data automation project was an excellent experience. The team understood our requirements clearly, transformed complex email data into meaningful insights, and delivered a reliable backend solution that significantly improved our workflow.”
“Bit&Bytes Team quickly understood our goals on SEO assistant project and implemented complex machine learning features with precision. there communication were clear, delivery was timely, and the overall collaboration was smooth and efficient. We're very satisfied with the results and would definitely work with them again.”
“We collaborated with Bit&Bytes team on the development of YourList, our real estate and investment networking platform. From the very beginning, they demonstrated a deep understanding of both the technical stack and the business vision behind the product. They helped us shape the MVP, ensuring smooth integration between backend and frontend. Throughout the process, they were proactive, detail-oriented, and always committed to delivering on time. Working with them seamless and highly productive, they truly went above and beyond to make the project a success.”
Frequently asked questions
Straight answers on cost, timelines, ownership and data.
Yes, for engagements involving PHI, and we use BAA-covered hosting and vendors.
Yes, using BAA-covered model providers or self-hosted models so PHI stays protected.
There is no official HIPAA certification. Compliance is shown through controls, policies and evidence, which we build and document.
Ready to talk about Compliance-Ready Development?
Book a short call with a senior engineer. No pitch deck, just a clear next step.
- We reply within 1 business day.
- NDA available on request
- You own all code from day one